
Your CCO Handles Strategy. Our AI Handles Everything Else.
The same AI tooling that powers the Auditbahn compliance team: available for in-house compliance officers. Questionnaires answered, vendors pre-screened, audit reports analyzed, policy gaps flagged. Automatically.
Everything That's Live Today
Six capabilities your compliance team gets on day one: no setup, no training data required.
Security Questionnaire Automation
AI fills customer security questionnaires using your company knowledge base: policies, certifications, controls. Draft in minutes, review and send. No more copy-pasting from a shared doc at 11pm.
Vendor Pre-Screening
Submit a vendor URL or document. AI screens against GDPR, SOC 2, HIPAA, and ISO 27001 signals: security posture, certifications, privacy policy, and subprocessors.
SOC 2 & ISO 27001 Report Review
Upload third-party audit reports. AI extracts key findings, exceptions, expiry dates, and subprocessors automatically. Gaps surface immediately, not buried in a 60-page PDF you read on a Sunday.
Policy Gap Detection
We track your controls against SOC 2, ISO 27001, HIPAA, and GDPR requirements. Drift is flagged before your next audit window, not discovered by the auditor on day one.
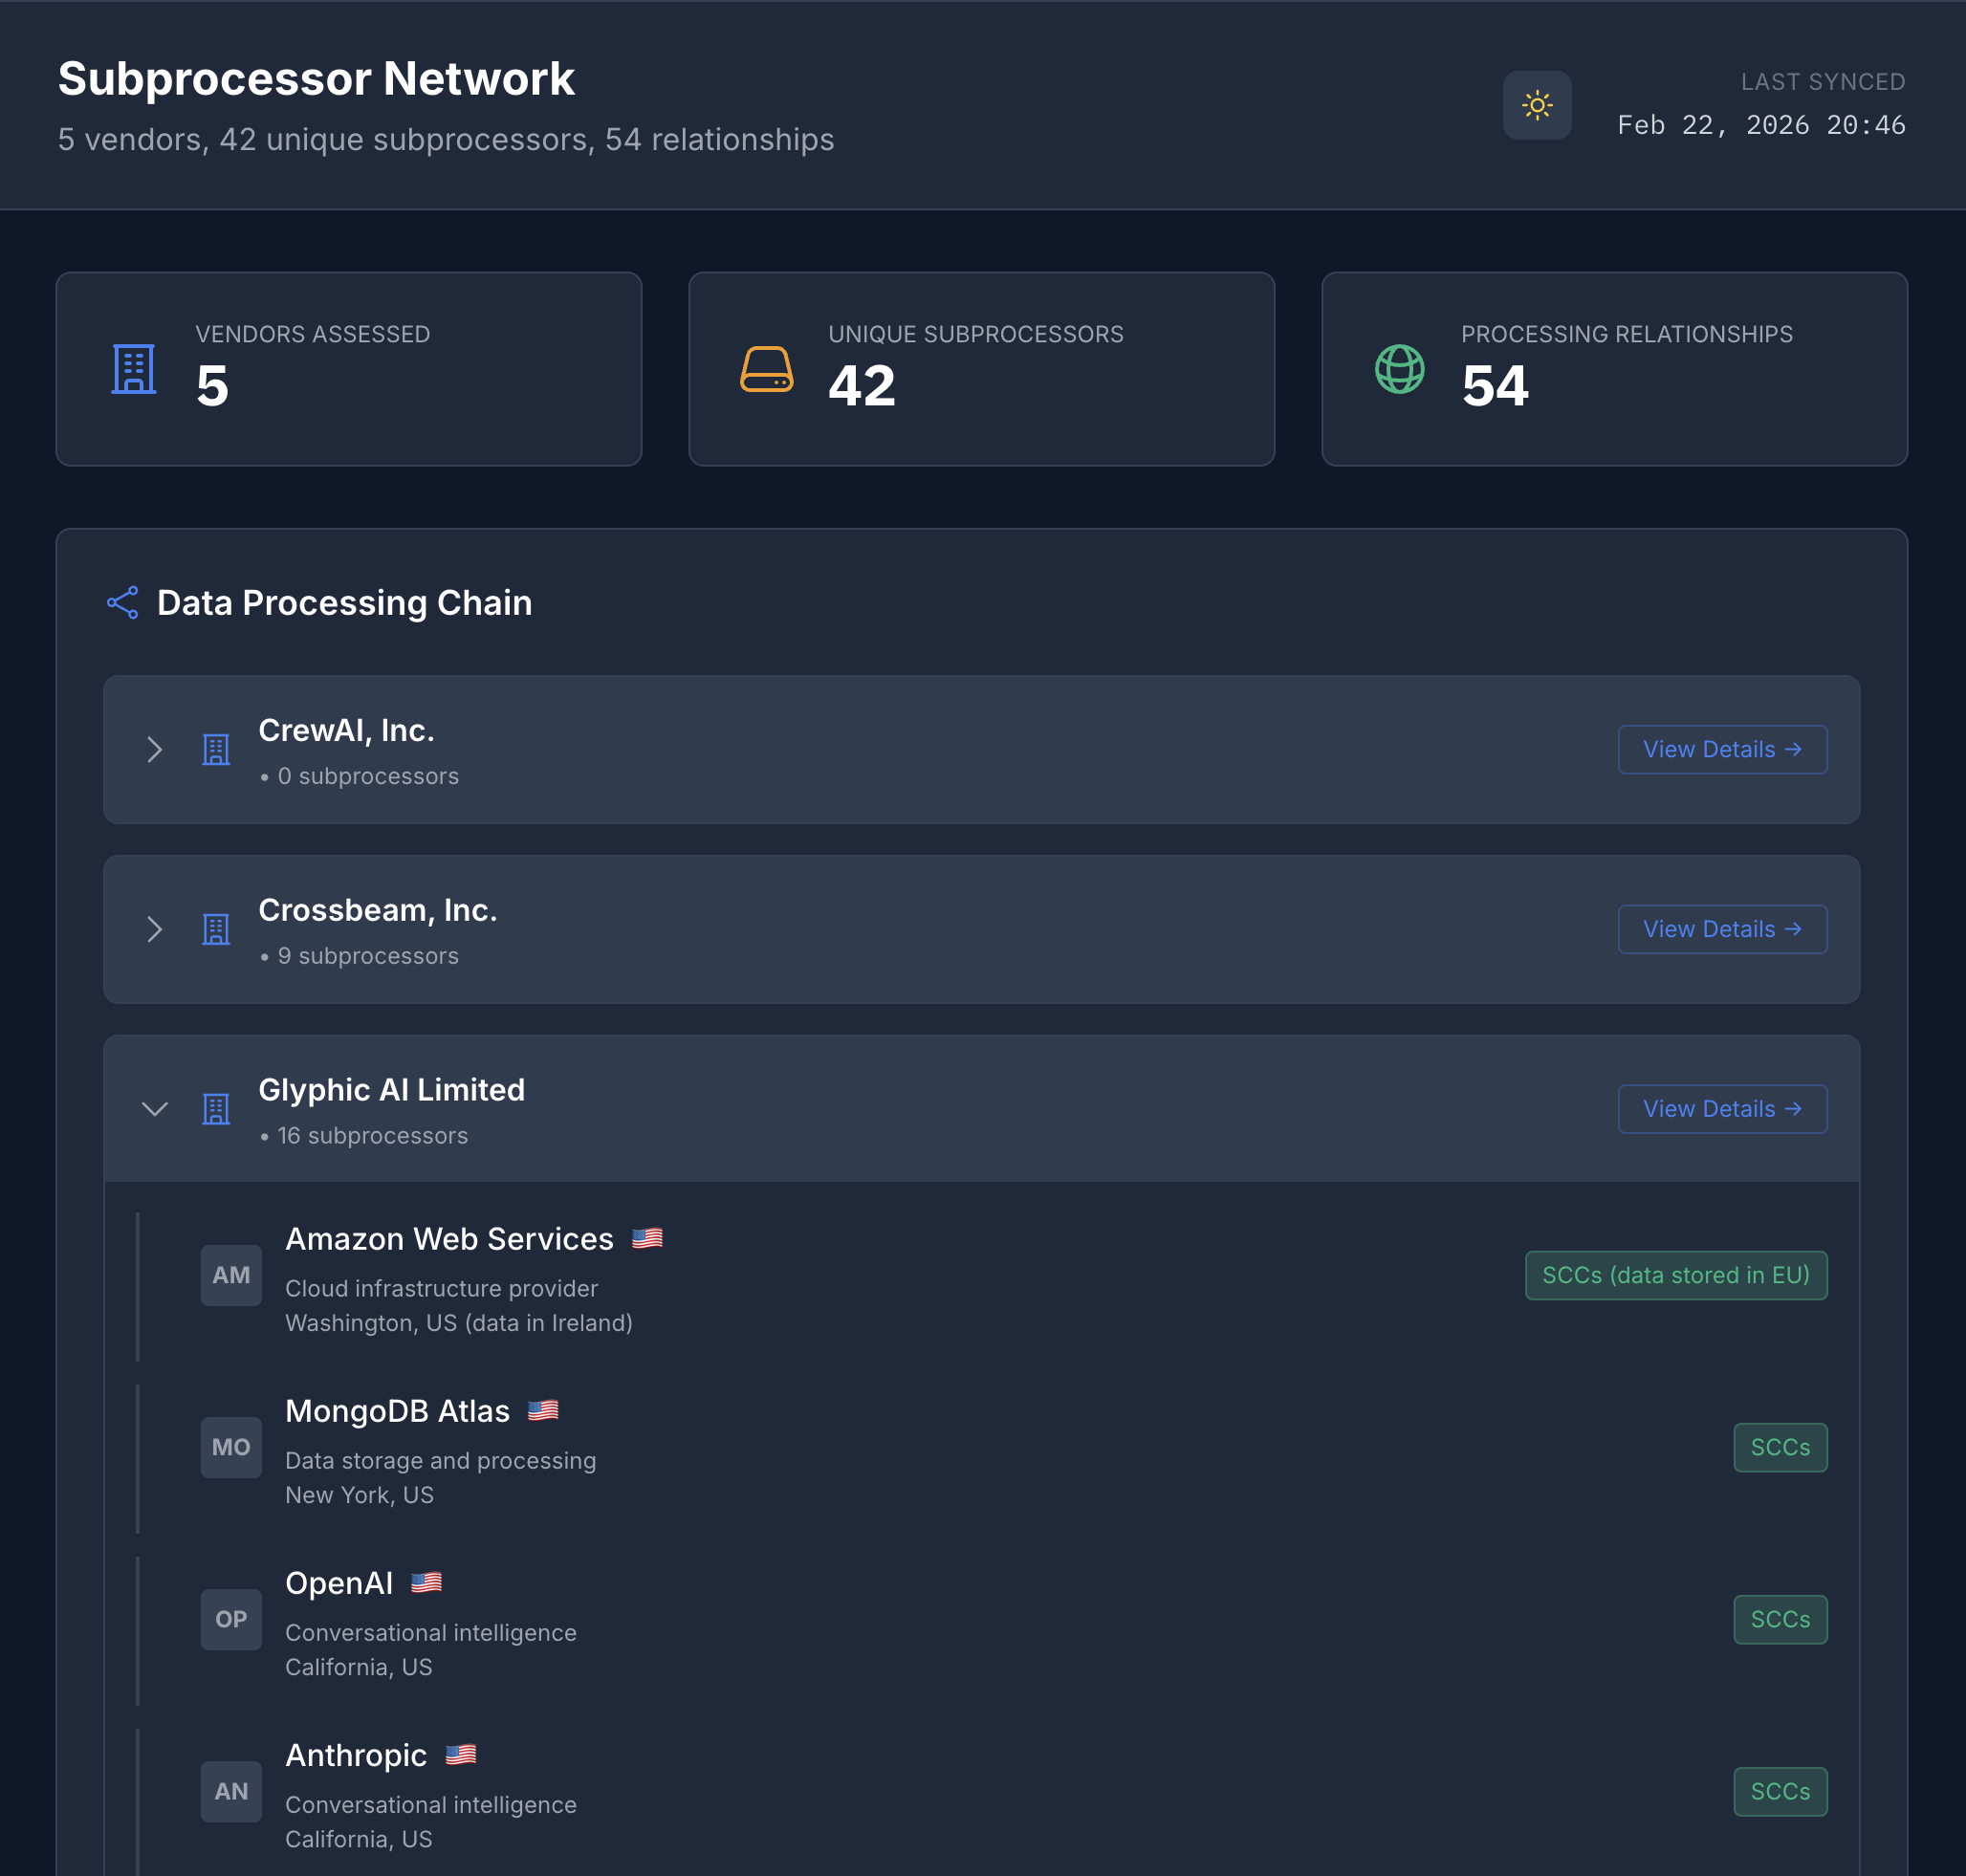
Subprocessor Chain Mapping
Your full vendor and subprocessor chain: mapped, live, and visualized. GDPR Article 28 compliant documentation generated automatically. See who processes what data, where, and when.
Compliance Health Dashboard
Real-time vendor risk scores, certificate expiry tracking, DPA status, and renewal alerts. Know your compliance posture at a glance, not after digging through five spreadsheets.
How It Works
Four steps from onboarding to staying compliant.
Connect Your Compliance Profile
Tell us your active frameworks (GDPR, SOC 2, HIPAA, ISO 27001) and upload your key documents: policies, existing vendor list, certifications. The platform tailors every assessment to your specific requirements.
Submit Vendors or Questionnaires
Drop in a vendor URL to pre-screen, upload a customer questionnaire to answer, or paste an audit report to review. The AI starts working immediately: no manual routing, no waiting for a human to pick it up.
Review AI-Generated Results
Get a fully reasoned output: vendor approval justification, questionnaire draft, or audit findings summary. Every decision is documented and traceable. Review, edit, approve. That's it.
Monitor Continuously
The platform tracks certificate expiry, vendor changes, and framework drift in the background. You get alerts before things become problems, not after an auditor or a customer surfaces them.
Full Visibility Into Your Vendor Ecosystem
Automated subprocessor chain mapping: every vendor relationship visualized and GDPR Art. 28 documented.
Be First to Access the Platform.
We're opening early access to a small group of compliance officers. Get full platform access, direct input into the roadmap, and a founder-level relationship with the team building it.
Request Early AccessContact us through our request form .